

Undefined: Top 7 Anomaly-Based Intrusion Detection Systems in the UK — 2026
In today's rapidly evolving digital landscape, UK enterprises face an unprecedented barrage of sophisticated cyber threats that traditional security measures struggle to contain. Anomaly-based intrusion detection systems (IDS) represent a paradigm shift in how organisations approach network defence, moving beyond reactive signature matching to proactive threat identification. These intelligent platforms continuously monitor network telemetry, establish behavioural baselines for users, devices and applications, and flag deviations that could indicate compromise or malicious activity. The main appeal for UK buyers is clear: improved detection of zero-day exploits and novel attack vectors, stronger support for GDPR and NIS2 compliance through enhanced monitoring and audit trails, and the ability to reduce dwell time via early warning of lateral movement. UK organisations tend to prefer solutions that combine high-fidelity detection with explainable alerts, scalable deployment across hybrid cloud and on-prem environments, clear integration paths into existing SIEM and SOAR stacks, and vendor support for tuning and managed detection services. Cost, ease of deployment, low false positive rates and strong local support are additional commercial preferences that drive purchase decisions in the British market.
Inception's AI took the time to understand this market in the UK · · How we pickWe may earn a commission on purchases. It never affects our rankings.
Top Picks Summary
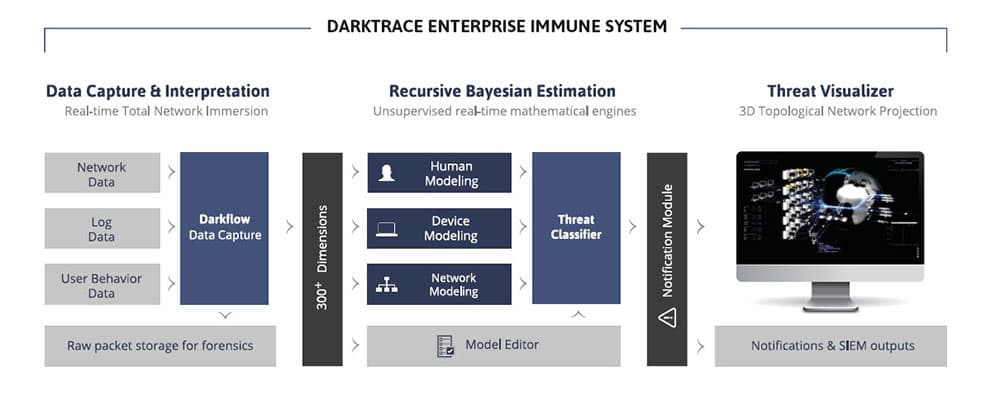
Darktrace Enterprise Immune System
Darktrace Enterprise Immune System tops the UK 2025 list for its self-learning AI that models normal enterprise behavior and autonomously adapts to novel threats, significantly reducing mean time to detection. Compared with Vectra, ExtraHop and Fidelis it delivers broader autonomous response capabilities and a premium but scalable licensing model that often lowers analyst hours and long-term operational costs for large, regulated UK organisations.
Estimated£50,000 – £150,000
Cisco Secure Network Analytics
Cisco Secure Network Analytics is a market leader for large enterprises, offering scalable NetFlow/sFlow-based behavioral analytics and tight integration with Cisco infrastructure that simplifies deployment for Cisco-heavy environments; for this use case (undefined) it is especially compelling when you already run Cisco networking gear. Technically it provides robust telemetry at scale and, compared with ExtraHop and Flowmon, often delivers better native integration into existing routes of remediation, while its licensing can be more complex but economically advantageous for large fleets.

Estimated£15,000 – £120,000
SolarWinds Security Event Manager
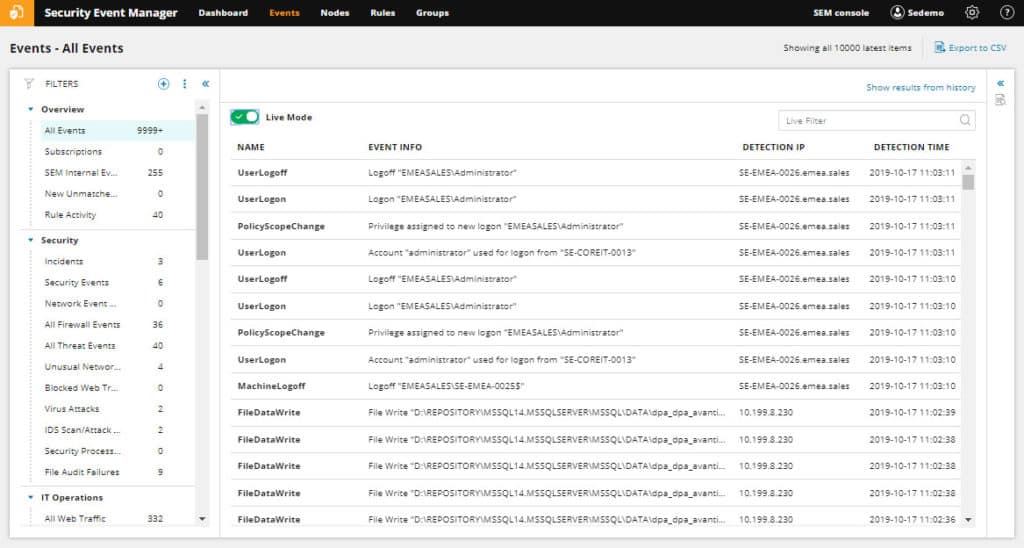
SolarWinds Security Event Manager is a cost-conscious SIEM that excels for mid-market organizations needing straightforward log collection, correlation, and automation; for this use case (undefined) it provides the quickest path to centralized log-based detection with predictable licensing. Compared to ExtraHop, Cisco, and Flowmon it lacks deep packet or flow-level analytics but offers a lower total acquisition cost and faster time-to-value than many NDR/XDR solutions, making it attractive where budget and simplicity matter most.
What research and authorities say about anomaly-based IDS
A growing body of research and guidance supports the value of anomaly-based detection approaches for identifying previously unknown threats. European cybersecurity authorities and independent studies highlight that behavioural and machine learning techniques can detect deviations that signature-based tools miss, particularly for lateral movement, encrypted traffic anomalies and novel exploit patterns. At the same time, research stresses the importance of model validation, ongoing tuning, explainability and human oversight to manage false positives and operational risk. For UK buyers, aligning anomaly detection with best-practice guidance from the UK National Cyber Security Centre and broader EU/ENISA recommendations helps demonstrate regulatory compliance and operational maturity.
Peer-reviewed studies show machine learning models can improve detection of zero-day attacks and reduce mean time to detection when combined with network telemetry analysis.
ENISA and other EU cybersecurity bodies recognise behavioural analytics as a complementary layer to signature-based defences, particularly for complex enterprise environments.
Research highlights the trade-off between sensitivity and false positives; organisations benefit from human-in-the-loop workflows and tuning to keep alert fatigue manageable.
Studies on encrypted traffic analysis demonstrate that flow-based anomaly detection can reveal malicious lateral movement without full packet inspection, helping privacy and compliance goals.
Evidence supports integrating anomaly detection outputs with SIEM and SOAR to accelerate investigation and automate validated response actions safely.
Frequently Asked Questions
Which anomaly-based IDS is best for autonomous threat containment?
Darktrace Enterprise Immune System is the best choice for autonomous containment because it features the Antigena capability, which takes automated actions to neutralise novel threats.
Does ExtraHop Reveal(x) Enterprise provide full packet-level visibility?
ExtraHop Reveal(x) Enterprise provides full-packet capture and forensic search capabilities, allowing for deep investigation across hybrid network environments.
How does Vectra AI Cognito Platform help reduce security team noise?
Vectra AI Cognito Platform reduces noise by using automatic risk scoring and prioritisation to focus your security operations centre on the highest impact threats.
What is the average user rating for Darktrace Enterprise Immune System?
Darktrace Enterprise Immune System holds an average rating of 4.6 out of 5 stars from users.
Conclusion
Anomaly-based intrusion detection has become a strategic requirement for UK organisations that need proactive, behaviour-driven protection and stronger compliance evidence. This guide profiles seven leading platforms suited to British enterprise environments: Darktrace Enterprise Immune System, Vectra AI Cognito Platform, ExtraHop Reveal(x) Enterprise, Cisco Secure Network Analytics, SolarWinds Security Event Manager, Stellar Cyber Open XDR Platform, and Kemp Flowmon ADS. Each product has strengths for different budgets, deployment models and maturity levels, but for a balance of advanced anomaly detection, explainability and strong enterprise support in UK contexts, Darktrace Enterprise Immune System stands out as the top choice among these options. We hope you found what you were looking for; you can refine or expand your search using the search box to compare features, deployment options and pricing in more detail.